AI Readiness Assessment: A Practical Framework for B2B Teams
Buying an AI tool isn't the same as being ready to use AI. A company can approve a copilot, connect a model to its CRM, and still lack the ownership, data controls, workflow discipline, and risk decisions needed for production use. The more useful question is not, “Which model should we buy?” It's, “Can our operating model absorb AI without creating unmanaged work, security exposure, or unreliable customer outcomes?”
That distinction matters because enterprise adoption is moving faster than operational maturity. In Cisco's 2025 AI Readiness Index, organizations were classified as 13% Pacesetters, 36% Chasers, 48% Followers, and 3% Laggards, with only modest movement from the prior years covered by the index (Cisco AI Readiness Index). A readiness review should therefore diagnose the conditions that make scaling possible, not reward a company for having experimented.
Why Most AI Readiness Assessments Miss the Real Problem
Most AI readiness checklists begin with technology. They ask whether the company has cloud capacity, model access, a data platform, or an approved vendor. Those questions matter, but they rarely reveal why a promising pilot fails after launch.
A tool can generate an answer without having a valid place in the process. If nobody owns the output, no team checks its quality, and no manager has authority to change the workflow, the deployment becomes another queue of exceptions. The model may be functional while the operation remains unprepared.
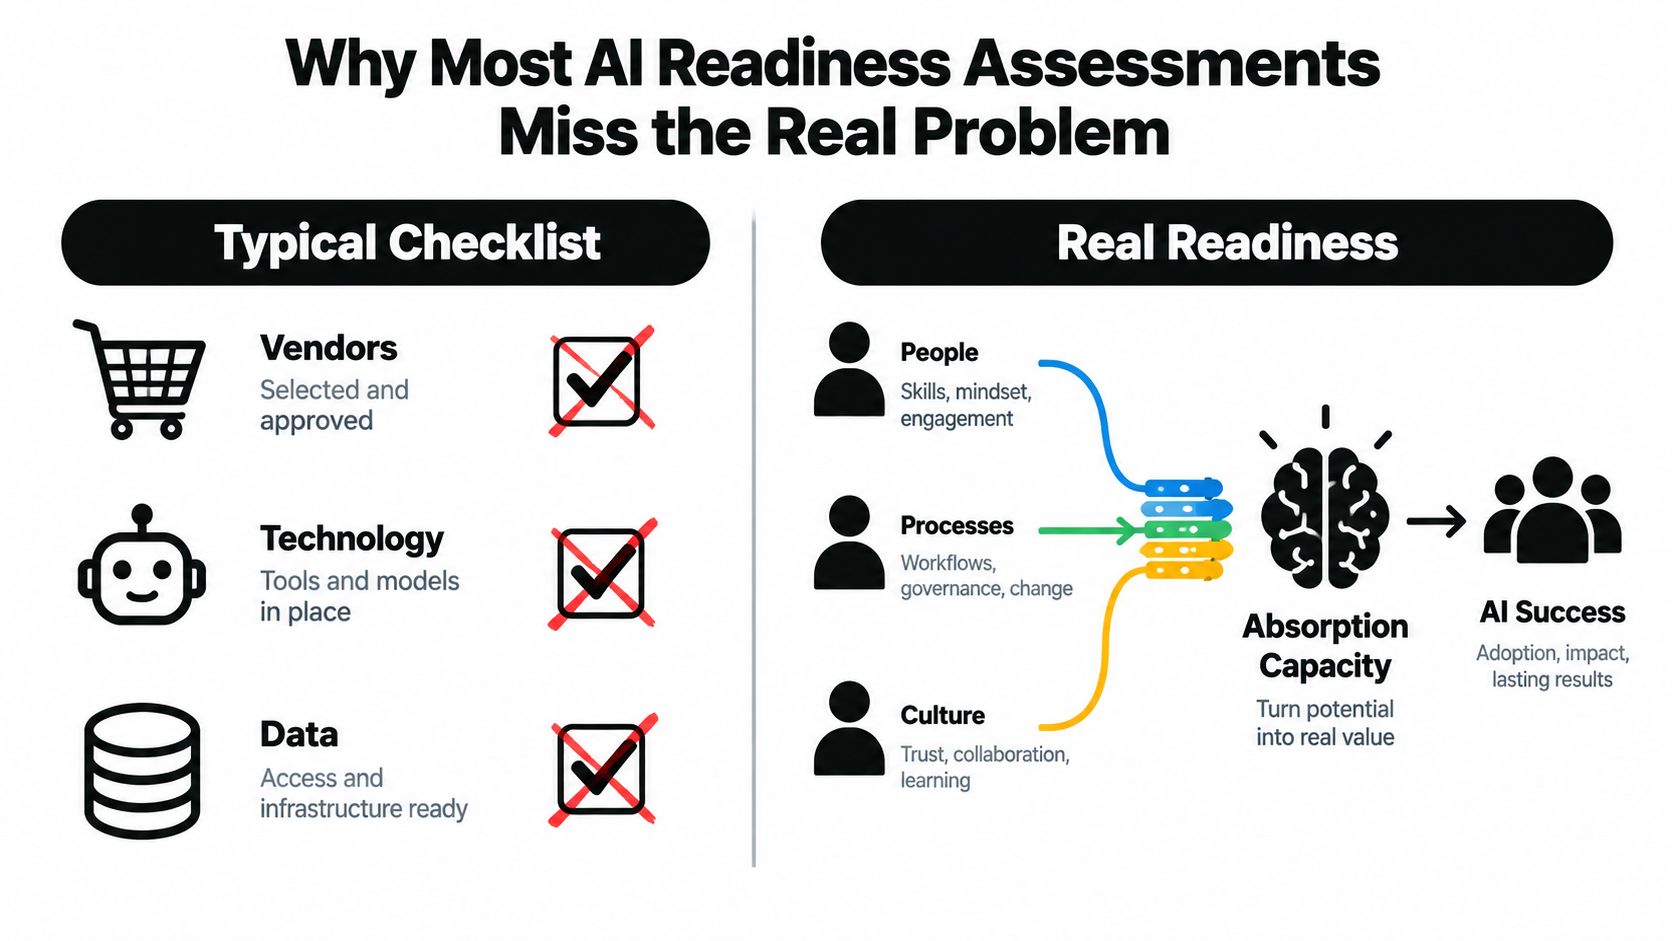
Readiness is an absorption capacity
I treat readiness as the organization's ability to adopt, govern, operate, and improve an AI-enabled workflow. That includes technical foundations, but it also includes decision rights, documented procedures, escalation paths, and a clear owner for the business result.
The leadership-versus-reality gap is especially revealing. Executives often feel ready because they sponsored the initiative, approved funding, or selected a vendor. Operators may see something very different: undocumented processes, inconsistent CRM fields, unclear data access, and no agreement about who reviews AI-generated work.
Practical rule: If the people who run the workflow can't describe how AI changes their daily decisions, the organization isn't ready for production scale.
Publicis Sapient's 2026 enterprise report captures this distinction. Seventy-three percent of leaders said AI was used regularly or across most business processes, but only 10% said AI was core to how the business operates (Publicis Sapient AI report, cited in PwC's readiness assessment resource). The same source reports that 42% said their organizations weren't set up to capture AI's value, while 22% identified the way their organization operates as the primary barrier.
What a serious assessment should expose
A useful review should make structural gaps visible:
- Ownership: Who is accountable for the workflow, output quality, risk decisions, and ongoing maintenance?
- Process stability: Is the workflow repeatable, documented, and measurable, or does it depend on individual judgment?
- Data control: Can the team identify the source, owner, permitted use, and quality condition of the data?
- Governance: Who can approve deployment, pause the system, escalate an incident, or reject a vendor?
- Adoption capacity: Can affected employees change their habits, and does management have a mechanism to reinforce that change?
Model quality becomes the main bottleneck only after these conditions are reasonably sound. Before then, the assessment is diagnosing the business system around the model.
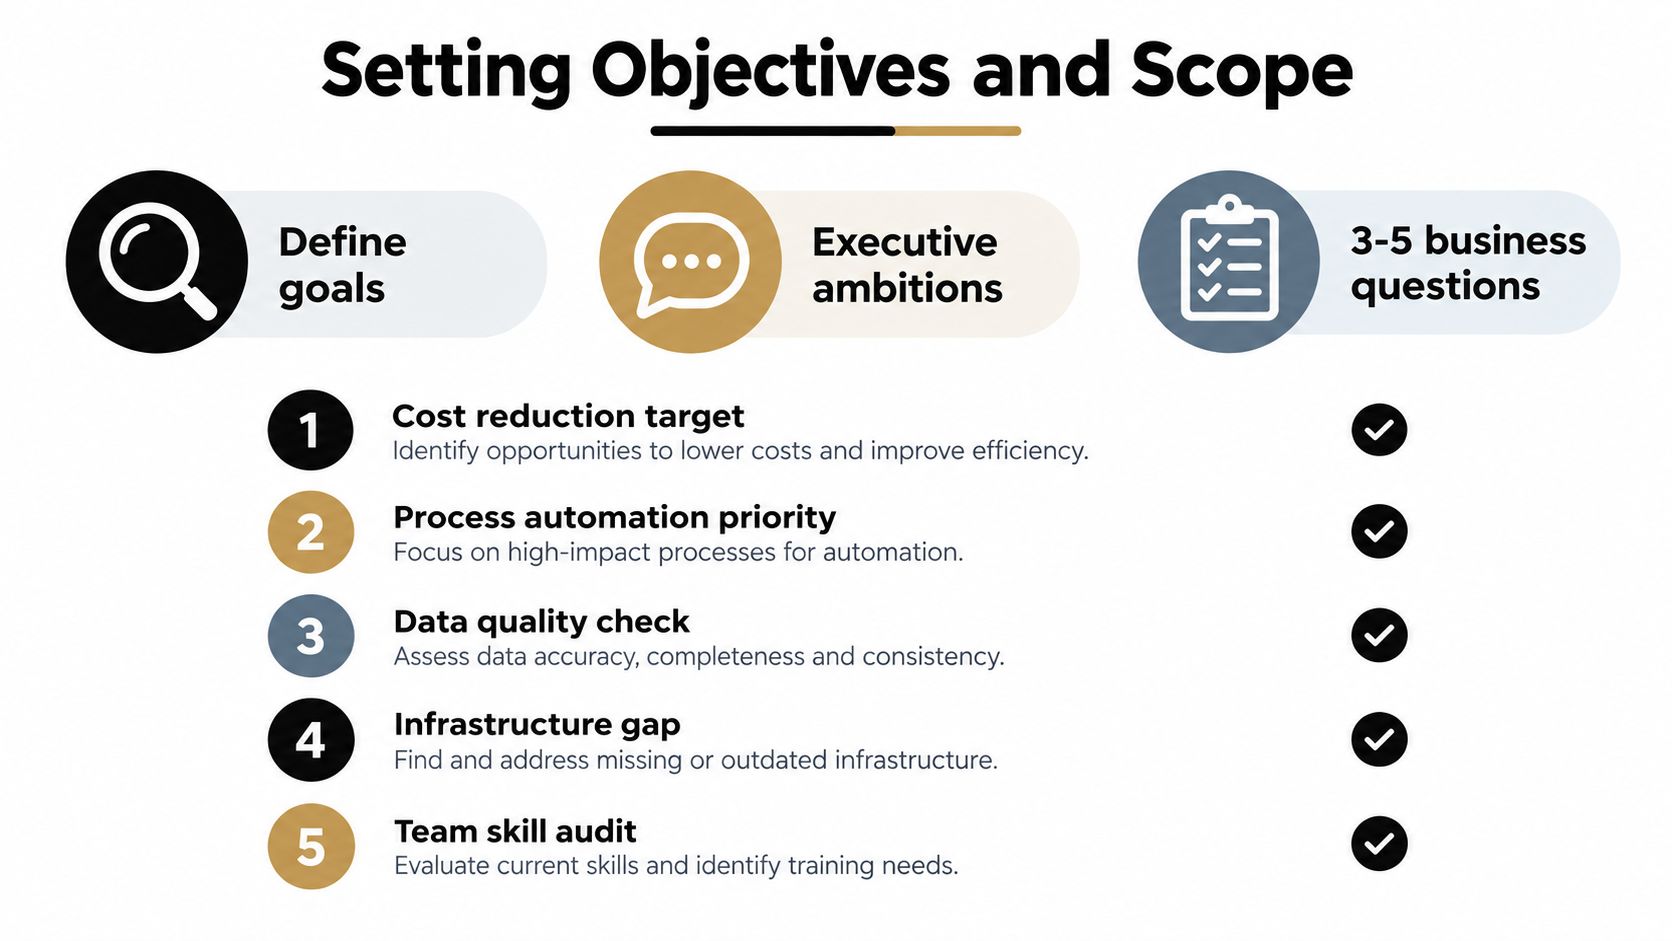
Setting Objectives and Scope for the Assessment
Start with business questions, not an inventory of fashionable AI applications. An executive statement such as “we need an AI strategy” is too broad to guide an assessment. Convert it into a small set of decisions the review must support.
Useful questions are concrete and testable:
- Which sales workflow creates avoidable delay or manual research?
- Which support process has enough repetition for assisted handling?
- Where do data-quality issues create rework or unreliable reporting?
- Which customer-facing use cases require formal risk review before launch?
- What must be true for a pilot to move into a supported production service?
These questions keep the review connected to outcomes. They also prevent the team from scoring capabilities that have no relationship to the company's immediate operating priorities.
Choose the people who can verify reality
The assessment needs a sponsor with budget authority, but an executive sponsor alone isn't enough. Include a process owner from each function in scope, a data or platform lead, a security or compliance representative where risk warrants it, and at least one constructive skeptic.
The skeptic has a specific job. They should challenge optimistic assumptions about data access, adoption, vendor capability, integration effort, and customer impact. A review that only interviews advocates produces a strategy document, not a reliable baseline.
Bound the work by department, workflow, or use-case cluster. A company-wide assessment sounds thorough but often produces generic ratings. A focused review of revenue operations, customer support, or internal knowledge management can identify dependencies that a broad questionnaire hides.
Write a one-page charter
Before technical interviews begin, publish a short charter containing:
- Objective: The decision or business outcome the assessment must support.
- Scope: Teams, systems, workflows, and data domains included.
- Exclusions: Areas deliberately left for a later review.
- Participants: Sponsor, process owners, technical leads, risk reviewers, and dissenting voices.
- Evidence standard: Documents, system records, access policies, workflow metrics, and observed demonstrations.
- Timeline: Interview, evidence collection, scoring, review, and decision dates.
- Decision rights: Who accepts the findings, funds remediation, approves a pilot, or stops an unsafe deployment.
This charter prevents scope drift. It also gives participants permission to say, “That question is outside this assessment,” instead of allowing every unresolved business problem into the same backlog.
Auditing Data and Infrastructure Readiness
Infrastructure readiness isn't a contest over GPU capacity. For most B2B and SaaS teams, the harder problem is predictable, governed data movement. The audit should show where information originates, how it changes, who can access it, and what breaks when a source or integration changes.
Use four layers.
Start with source systems
Create an inventory of CRM, billing, support, product analytics, marketing automation, HR, and document systems. For each source, record the business owner, technical owner, data categories, update pattern, retention expectation, and known quality issues.
Look for orphaned schemas, duplicated customer records, undocumented event streams, and fields that different departments interpret differently. A field called “customer status” can mean contract state to finance, lifecycle stage to marketing, and support priority to customer success. That ambiguity matters more than the presence of a modern data warehouse.
Trace the integration plumbing
Map ETL jobs, reverse ETL flows, webhooks, APIs, middleware scenarios, and manual exports. Confirm dependencies, failure handling, monitoring, and API rate limits. If a pipeline fails, someone should know what failed, what data was affected, and who owns recovery.
A practical data-quality review should examine completeness, freshness, consistency, validity, and lineage. Teams that need a more formal control process can use this data quality assurance framework to organize checks and assign ownership.
Inspect storage, compute, and access
Document warehouses, lakes, object storage, vector stores, model endpoints, and processing environments. The question isn't whether the architecture looks advanced. It's whether the environment can support repeatable workloads with appropriate logging, cost controls, backups, and recovery procedures.
Then verify role-based access for both inference and training pipelines. SaaS companies need particular care around tenant isolation, personally identifiable information in shared models, test data, and prompts that may contain confidential customer content.
An AI system can be technically available and operationally unusable if the team can't prove where its inputs came from or who was allowed to see them.
The audit output should be a working register, not a slide with architecture icons.
| Field | What to record |
|---|---|
| Data source | System, dataset, event stream, or document repository |
| Owner | Business and technical accountability |
| Quality condition | Known completeness, consistency, freshness, or validity issues |
| Integration path | APIs, pipelines, middleware, exports, and dependencies |
| Access model | Roles, environments, tenant boundaries, and sensitive fields |
| Integration debt | Undocumented work, manual steps, brittle dependencies, or missing monitoring |
| Readiness action | The specific control, repair, or decision required |
UNESCO's guidance supports combining quantitative and qualitative indicators across legal, social, economic, educational, scientific, and technological dimensions, rather than relying on a simple maturity survey (UNESCO Readiness Assessment Methodology). That principle applies directly to enterprise audits. Evidence should come first. Scoring comes after the baseline is credible.
Evaluating Processes, Skills, and Governance Ownership
AI projects often collapse in the space between departments. The process owner assumes IT will manage the model. IT assumes the business will define acceptable outcomes. Legal expects security to identify the risk, while security waits for a documented use case.
Evaluate three layers separately, then examine how they connect.
Process maturity comes first
List the workflows the initiative depends on, such as lead routing, proposal creation, ticket triage, invoice exception handling, or renewal forecasting. Rate each workflow using evidence:
- Is the procedure documented?
- Is execution repeatable?
- How often do exceptions occur?
- Does one person own the end-to-end result?
- Do the inputs and outputs have agreed definitions?
A workflow held together by tribal knowledge isn't ready for automation because it happens frequently. If the owner changes regularly or every operator handles exceptions differently, AI will reproduce inconsistency at greater speed.
Map capability, not headcount
Count less and map more. A team may have plenty of technical employees but still lack data stewardship, prompt evaluation, vendor management, model operations, change enablement, or customer-facing AI fluency.
For customer-facing technical teams, this resource on AI skills for PreSales engineers offers a useful lens for thinking beyond generic training. The assessment should connect each capability to a workflow and identify whether the skill is available internally, assigned to a vendor, or missing entirely.
Test governance ownership
Governance is real only when a named person has authority. Ask who approves model selection, permitted data use, evaluation criteria, security exceptions, incident escalation, and retirement decisions. A committee can advise, but it shouldn't replace accountable decision-making.
| Dimension | What to Evaluate | Evidence Required | Common Failure Signal |
|---|---|---|---|
| Process | Documentation, repeatability, exceptions, owner stability | SOPs, workflow records, interviews, observed execution | Operators use different undocumented methods |
| Skills | Data stewardship, evaluation, operations, vendor management, change enablement | Capability map, role descriptions, training records | One enthusiastic team carries the entire initiative |
| Governance | Approval, risk escalation, access, monitoring, retirement | Policies, decision logs, ownership matrix | A sponsor lacks budget authority or review standing |
Leadership may appoint an AI sponsor who has no budget line, no veto over vendor selection, and no standing in security reviews. That isn't sponsorship. It's a title without operating power. A concise AI governance best practices guide can help turn abstract responsibility into explicit controls and decision rights.
The final output should fit on one page. Separate blockers, dependencies, capability gaps, and cultural resistance. “The team is skeptical” is not equivalent to “the team lacks a safe escalation path.”
Scoring Readiness with a Weighted Maturity Model
A flat scorecard is easy to explain and often misleading. If every dimension receives equal weight, a polished strategy presentation can offset weak data lineage, unclear governance, or fragile integrations. The result looks balanced because the arithmetic is balanced.
A weighted model reflects dependency and risk. One practical starting structure assigns 30% to data and infrastructure, 30% to processes and governance, 20% to skills, and 20% to strategic alignment. These are assessment design choices, not universal facts. A regulated business may place more emphasis on controls, while a horizontal SaaS company may weight integration and process reliability more heavily.
Define maturity through evidence
Avoid labels such as “advanced” unless they describe observable conditions.
- Level 1, ad hoc: Work depends on individuals and undocumented decisions.
- Level 2, repeatable: A named owner follows a documented approach.
- Level 3, measured: The team tracks performance and exceptions.
- Level 4, governed: Controls, approvals, monitoring, and escalation are established.
- Level 5, optimized: The organization improves the capability using reliable operational evidence.
The score should answer, “What can we prove?” A Level 4 alignment score supported only by executive interviews is weaker than a Level 2 score supported by process records, ownership documents, and observed behavior.
Use the score to reveal the constraint
Consider a team that reports Level 4 strategic alignment but has Level 1 data lineage. Under a flat average, the strong alignment rating may soften the apparent risk. A weighted model keeps the data dependency visible, especially when the proposed use case relies on customer, product, or financial information.
| Dimension | Weight | Current Level (1-5) | Weighted Score | Evidence |
|---|---|---|---|---|
| Data and infrastructure | 30% | 1 | 0.30 | Partial source inventory, weak lineage records |
| Processes and governance | 30% | 2 | 0.60 | Some SOPs, unclear approval ownership |
| Skills | 20% | 2 | 0.40 | Technical interest, limited operational coverage |
| Strategic alignment | 20% | 4 | 0.80 | Clear use-case priorities and executive sponsorship |
The arithmetic isn't the conclusion. The heatmap is. Publish each dimension, its evidence, its confidence level, and its remediation owner. Include a non-executive reviewer in the calibration session. Deloitte reports that 42% of companies believe their strategy is highly prepared for AI adoption while feeling less prepared in infrastructure, data, risk, and talent (Deloitte State of AI in the Enterprise). Independent scoring helps prevent confidence from becoming the evidence.
For investment decisions, connect the maturity result to a documented cost-benefit analysis framework. Don't allow a single readiness number to decide a program that has several different risk profiles.
Building a Prioritized Remediation Roadmap
A readiness score becomes useful only when it determines what the organization fixes, in what order, and who must prove completion. Convert every material gap into a remediation item with one accountable owner, known dependencies, an expected business effect, and an exit criterion that another reviewer can verify.
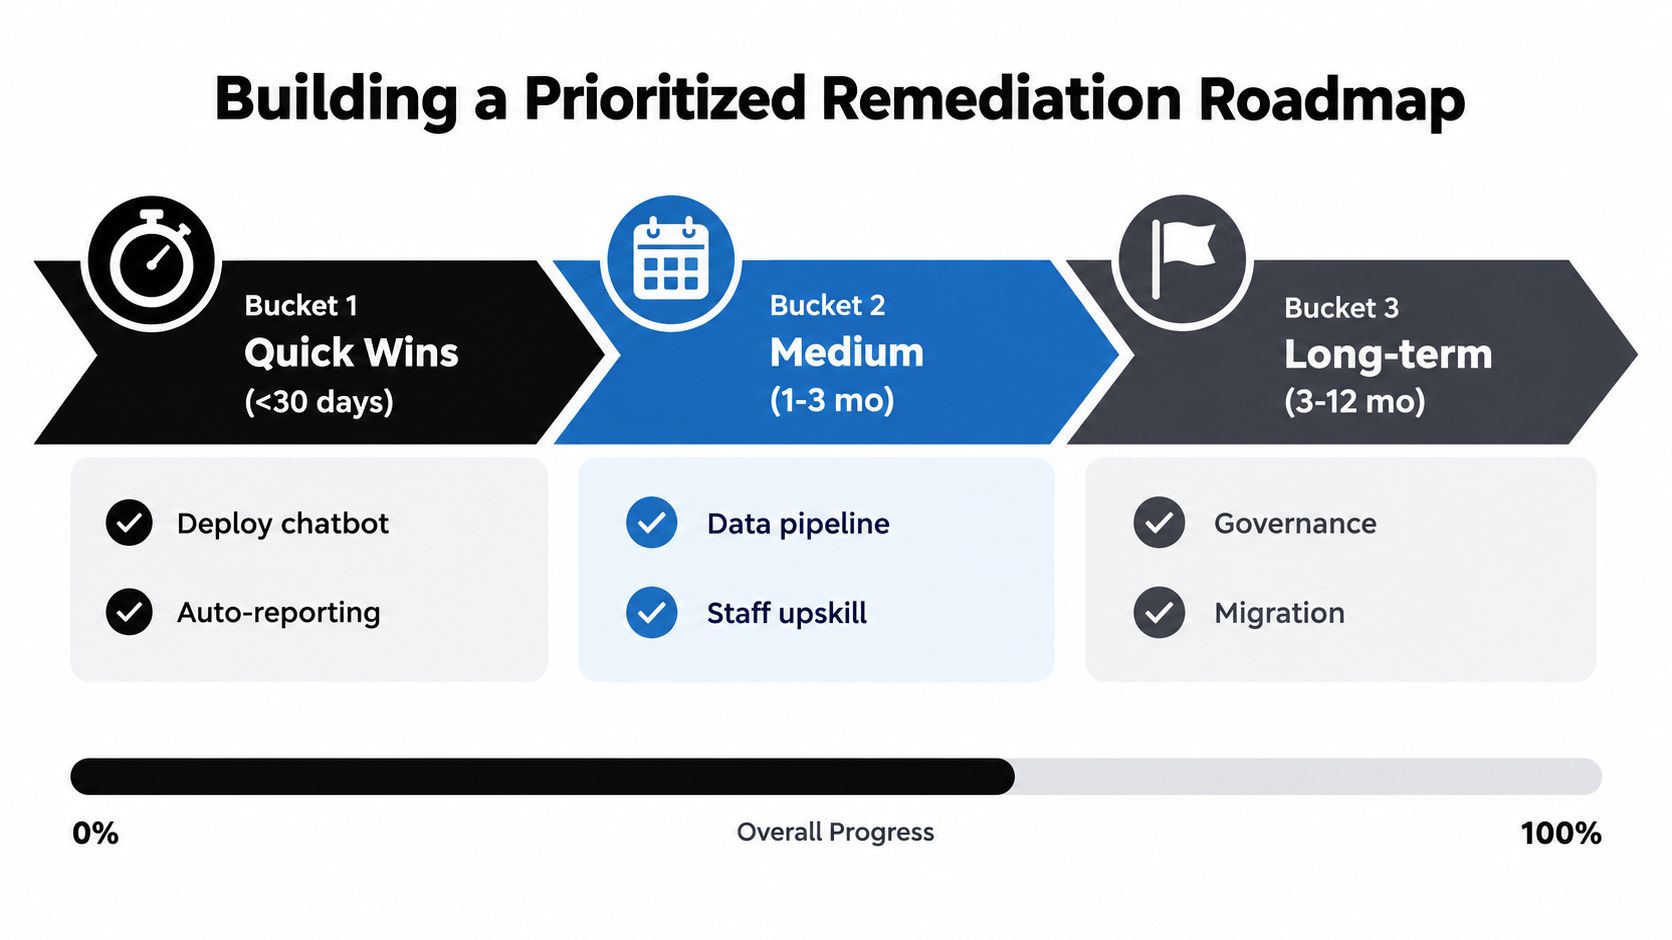
Use three practical buckets:
- Quick wins, under 30 days: Clarify ownership, document a workflow, create an initial source register, or approve an evidence standard.
- Structural fixes, within one quarter: Repair a data pipeline, formalize vendor due diligence, establish evaluation procedures, or ratify a governance charter.
- Foundational investments, over six to twelve months: Redesign a fragmented architecture, migrate critical data, build sustained operations capability, or establish enterprise control systems.
Prioritize dependencies, not excitement
Rank each item by business impact, dependency risk, and cost of delay. The scoring supports a defensible sequence. It should not create false precision. A missing data-access policy may attract less attention than an internal chatbot, yet it can block every customer-facing workflow that depends on the same data or approval path.
EY's 2025 AI GRC survey identifies integration with existing IT, talent shortages, and regulatory constraints as barriers to scaling AI. It also reports that 70% of CEOs said they reached their cloud setup “by accident rather than design”, a warning that inherited architecture may not support deliberate AI expansion (EY AI GRC survey). Treat architecture, access, and control requirements as delivery dependencies. They determine whether a pilot can become an operating process.
A remediation item without a dependency owner will usually wait behind the more visible project. Record which decision, system, team, or control must be ready first.
A workable 90-day sequence
| Period | Milestone | Accountable owner | Exit criterion |
|---|---|---|---|
| Weeks 1-2 | Document critical data sources and owners | Data lead | Source register reviewed by business owners |
| Weeks 3-4 | Map lineage and access for the selected workflow | Platform and security leads | Access path and sensitive fields documented |
| Weeks 5-6 | Draft and ratify governance charter | Risk or operations lead | Approval and escalation responsibilities signed |
| Weeks 7-8 | Establish vendor due diligence requirements | Procurement and security | Review checklist accepted for the target vendor |
| Weeks 9-10 | Select one pilot workflow | Process owner | Baseline, user group, and success conditions recorded |
| Weeks 11-12 | Run controlled pilot review | Sponsor and process owner | Model risk review, operating procedure, and decision recorded |
Keep workstreams small enough to manage and explicit enough to audit. Owners should report evidence rather than activity. “Held three meetings” does not demonstrate readiness. “Signed data access policy” does.
EY's 2025 survey found only 10% of organizations were fully prepared for AI system audits, 28% were fully compliant with the EU AI Act, one-third lacked well-defined AI governance models, and 18% had clearly defined data governance responsibilities. These findings support the sequence: establish governance, ownership, and evidence before pilots become operational commitments. The leadership team may want visible experimentation first, but unresolved control gaps can turn a promising pilot into an unmanaged production obligation.
Tracking KPIs and Sustaining Readiness Over Time
Readiness is an operating discipline, not a document that goes stale after a steering committee meeting. KPIs should show whether the organization can deploy and control AI reliably, rather than count new experiments.
Use four KPI families, with a named owner and a fixed review rhythm.
| KPI | Owner | Target Example | Review Cadence |
|---|---|---|---|
| Data quality | Data lead | Critical sources have documented quality checks and owners | Monthly |
| Process automation rate | Process owner | Approved workflow steps are measured before and after automation | Monthly |
| Governance maturity score | Risk or operations lead | Required approvals, monitoring, and escalation records are current | Monthly, with quarterly assurance |
| Skill coverage | People or capability lead | Critical workflows have assigned operational and data capabilities | Quarterly |
Set targets against the organization's data, risk profile, and operating model. A copied benchmark can create false confidence. Each score should describe the system's condition and identify the evidence supporting it.
A monthly readiness standup should cover open blockers, changed dependencies, incidents, data-quality exceptions, adoption feedback, and overdue decisions. A quarterly board scorecard can show the heatmap, remediation status, use-case portfolio, and unresolved risk. Place confidence ratings beside maturity ratings so leadership can see where evidence remains weak.
Reopen the full assessment after a material vendor change, a new sensitive data source, a major workflow redesign, or a regulatory shift. EY's findings on audit preparation, compliance, governance models, and ownership, cited earlier, show why controls require active maintenance rather than one-time approval.
The leadership team may see a high maturity score while operators still lack a current procedure, a clear escalation path, or an accessible audit record. Make that gap visible. Every score should link to an owner, a dated artifact, and a decision record. If reviewers cannot open the evidence during the review, the capability is less mature than the score suggests.
MakeAutomation helps B2B and SaaS teams assess process readiness, technology compatibility, data integrity, team capability, compliance, and security before scaling AI workflows. Visit MakeAutomation to review the available assessment and get practical support for documenting, prioritizing, and implementing your next automation initiative.